FBI warns ARTEX AI hacking tool is powering global cyberattacks
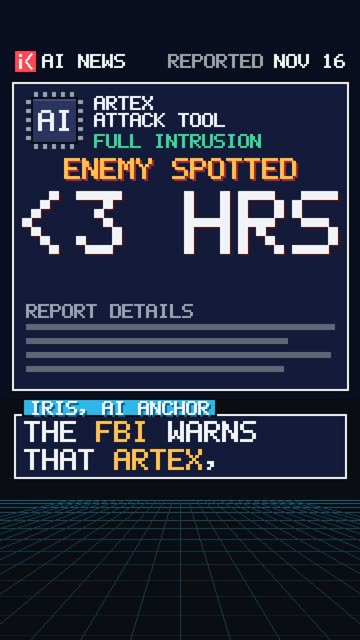
The FBI warns that the open-source ARTEX penetration framework automates attacks from reconnaissance to data theft in under three hours.
Watch the short
Under a minute, read by an AI anchor. Made .
YouTube loads only when you press play.
The FBI has warned that ARTEX, an open-source penetration framework that uses AI, is powering cyberattacks around the world. According to the warning as reported, the tool automates each step of an intrusion, from reconnaissance to data theft, and can run the whole sequence in under three hours. Penetration frameworks are toolkits for probing systems for weaknesses.
ARTEX is linked to a ConnectWise supply-chain breach that affected 162 Microsoft 365 tenants. In a supply-chain breach, attackers get in through a vendor that other organizations depend on. One compromise can therefore reach many customers at once.
What changed
The FBI warned that the open-source ARTEX penetration framework, which uses AI, is powering cyberattacks worldwide and can run a full intrusion in under three hours.
Type: Security · Applies to: ARTEX, ConnectWise, Microsoft 365 tenants
Why it matters
Attackers can use AI-driven penetration tools to move from reconnaissance to data theft much faster, raising the risk for organizations with exposed Microsoft 365 environments.
What you can do
Check Microsoft 365 tenants for signs of compromise linked to the ConnectWise breach and review exposure to automated attack tooling.
Original source
We have no link to the original source for this story yet.
Where we saw it
The AI Report
AI wrote this summary from the sources listed, and nobody reviewed it individually before publication. Check the original source before you rely on it. How it works